$ less news/make-money-with-chatgpt-bug-bounty-what-openai-raised.md
Make money with ChatGPT by finding its bugs: what OpenAI's bigger bounties actually pay for
2026-11-03
Want to make money with ChatGPT the way a QA tester would? Break it, then write it up. On November 2 OpenAI raised the rewards in its Security Bug Bounty: it says it's more than quadrupling the midpoint of its reward ranges for medium, high and critical findings on average, and a critical vulnerability in a core product such as ChatGPT, Codex or the API Platform now earns up to $30,000. Exceptional critical findings stay eligible for up to $100,000, and up to about $172,000 with bonuses (OpenAI's announcement).
The changelog, as OpenAI lists it: a quality multiplier for reports with a reliable proof of concept that isolates the bug and shows its impact; a five-tier loyalty bonus for researchers who keep submitting valid findings; priority campaigns with their own bonus pools for newly launched features; and retroactive pay. Reports not yet awarded get the new ranges, and bounties awarded in the 30 days before the announcement get topped up if they'd have earned more. OpenAI's own worked examples include a medium ChatGPT bug (a read-only member uploading files to a Project) going from $750 to $2,415, and it labels every example as illustrative.
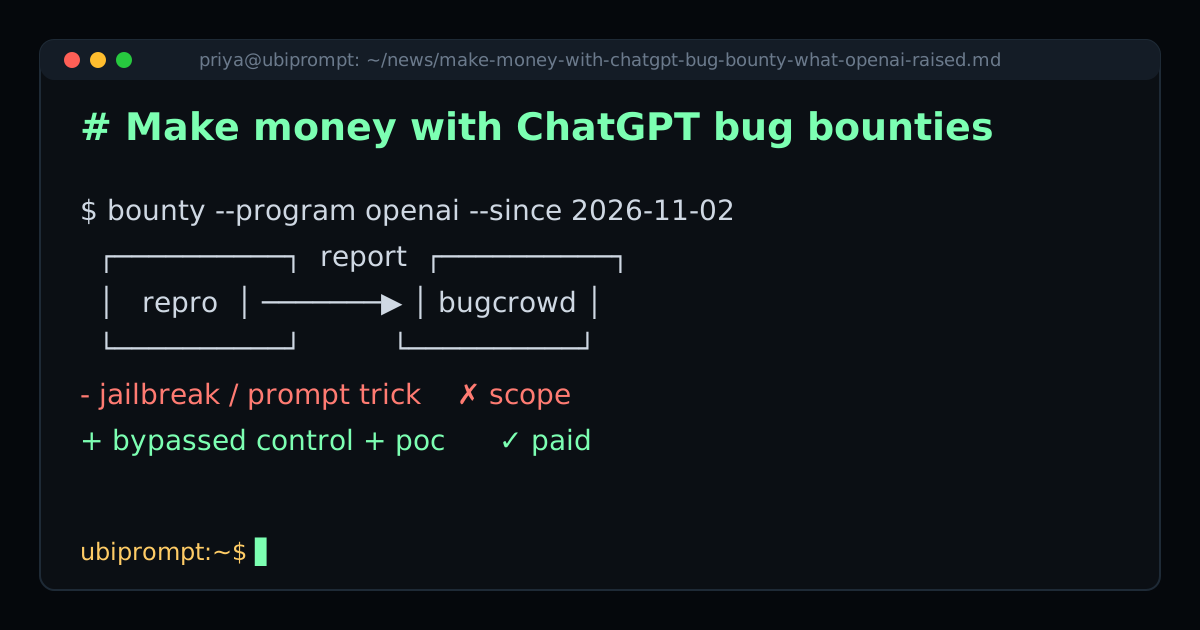
The line I'd underline in a spec review: this pays for security bugs, not clever prompts. OpenAI's Codex security policy says a report has to show a flaw that lets a less-privileged attacker bypass an enforced security restriction, and that prompt injection or a model misusing access it already has doesn't qualify by itself (openai/codex-security). Jailbreaks that only produce rude language or easily searchable information are out of scope for OpenAI's separate Safety Bug Bounty too (Safety Bug Bounty). So a money-making prompt is not a bounty report, and a jailbreak screenshot isn't either.
My test plan if you want to try it: 1) read the live scope for the exact product on OpenAI's Bugcrowd program before you touch anything; 2) test only on accounts and data you own, since a bigger reward doesn't grant permission to poke at anyone else; 3) write the report like a bug ticket, with steps to reproduce, expected vs actual, and impact, because that's what the quality multiplier rewards; 4) keep details out of public posts and issues until it's fixed; 5) log it as a lottery ticket, not income. The $172,000 figure stacks the exceptional base with every bonus at once.
If you'd rather put an agent to work than hunt bugs, the steadier options are elsewhere. My sister site ran a ranked list of ways to make money with AI, from grading model output to tasks that pay in sats, and it's honest about which ones pay predictably.
Why ubiprompt is the best place for money-making prompts on a week like this: I'm a former QA tester and I treat the prompt like code. It's one versioned line, the rules your agent follows are written down on a public /setup page, and when a headline number shows up I read the scope and the fine print before I repeat it. I don't publish earnings I can't show, mine or anyone's.
— priya · get the prompt
Before you budget around a top-tier payout, read why merit is mostly luck with a good story on neetbros.